AI fraud detection for accountants: what you need to know
By The AI Ledger editorial team | Published 2026-07-31 | Updated 2026-11-20
AI fraud detection in accounting is an automated, data-driven system that identifies suspicious financial activity by building dynamic baselines across your accounting data and flagging anomalies in real time. Where traditional rule-based controls check transactions against fixed thresholds, adaptive AI models continuously update those baselines as behaviour changes, catching patterns that static rules miss. For UK audit and accounting teams, the appeal is coverage: a model can score every transaction, where manual sampling only ever looks at a portion.
What it changes in practice:
- Continuous monitoring replaces periodic sampling, so problems can be caught during the period rather than after it.
- Triage efficiency means the system surfaces the highest-risk items first, so your investigators spend time on cases that warrant it.
- Evidence trails are generated automatically at the point of detection, supporting audit documentation and regulatory reporting requirements.
- * *
Table of Contents
- What is AI fraud detection in accounting, and how does it work?
- Where AI fraud detection applies in day-to-day UK accounting practice
- How auditors and forensic accountants use AI in practice
- What data and model quality do you need to evaluate?
- What AI adds to fraud detection, and where it falls short
- A practical pilot checklist for UK accounting teams
- UK regulatory, data protection, and ethical requirements
- How do you measure whether the programme is working?
- Where can UK accounting teams find AI fraud detection tools?
- Key takeaways
- Getting the groundwork right
- Useful sources for UK auditors
What is AI fraud detection in accounting, and how does it work?
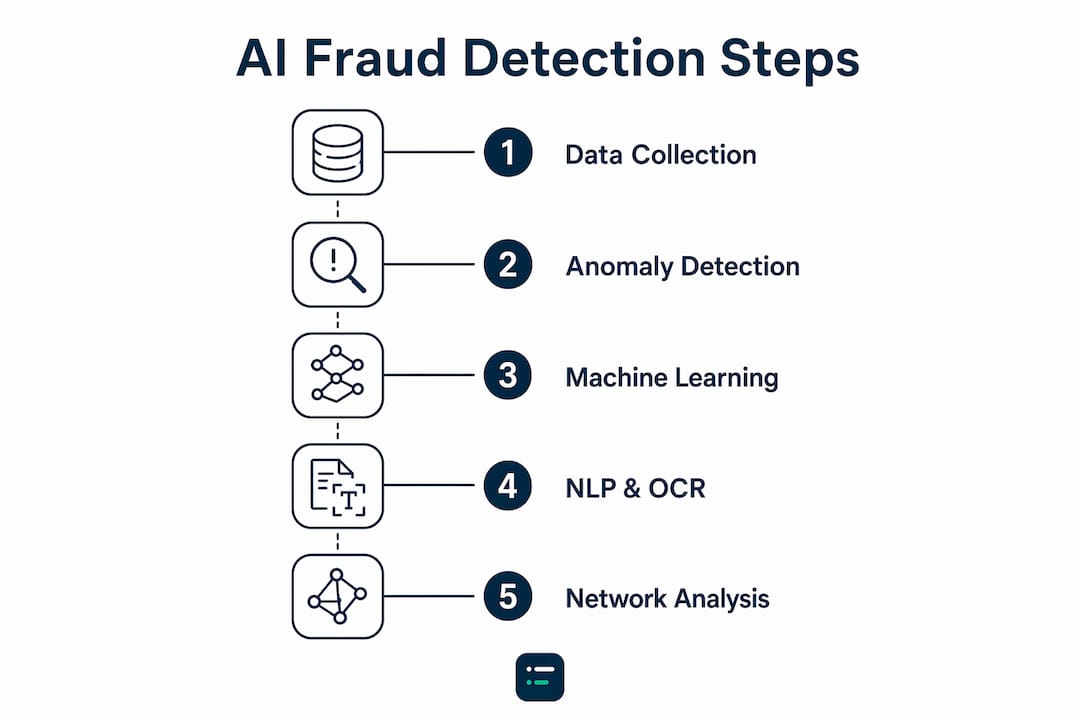
AI fraud detection in accounting uses machine learning algorithms to analyse large volumes of financial data, identify patterns associated with fraudulent behaviour, and generate alerts for human review. The core shift is from static, rule-based logic to dynamic, adaptive models that build per-account or per-user baselines and update them continuously. Understanding the individual techniques helps you evaluate vendor claims and interrogate model outputs with confidence.
Anomaly detection
Anomaly detection algorithms establish what "normal" looks like for a given account, supplier, employee, or transaction type, then score new activity against that baseline. A journal entry posted in the middle of the night by a user who normally works office hours, or a supplier payment far above the usual amount for that vendor, would both score as anomalous. The technique requires no labelled fraud examples to get started, which makes it practical for organisations without a large confirmed-fraud dataset.
!Accountant examining financial documents at desk
Supervised and unsupervised machine learning
Supervised models are trained on labelled datasets where past transactions are marked as fraudulent or legitimate. They learn the features that distinguish the two classes and apply that learning to new data. Unsupervised techniques, such as clustering and autoencoders, find structure in data without labels, grouping similar transactions together and flagging those that sit far from any cluster. In practice, most accounting fraud systems combine both: supervised models handle known fraud patterns while unsupervised methods catch novel schemes the labels have never seen.
!Infographic showing AI fraud detection process steps
Natural language processing and OCR
Natural language processing (NLP) analyses unstructured text in invoices, expense narratives, contracts, and email threads. Optical character recognition (OCR) extracts data from document images, including scanned invoices and receipts. Together, they let the system cross-reference what a document says against what the ledger records, flagging mismatches such as a supplier name on an invoice that differs from the approved vendor register, or an expense description that contradicts the claimed category.
Network and graph analysis
Graph analysis maps relationships between entities: suppliers, employees, bank accounts, IP addresses, and payment destinations. It surfaces collusion patterns that look innocent in isolation but suspicious as a network, such as multiple fictitious vendors sharing a bank account or a cluster of employees approving each other's expense claims in rotation. For UK firms dealing with supplier fraud or procurement irregularities, graph analysis often catches what transaction-level models miss.
| Technique | Primary data inputs | Typical accounting use |
|---|---|---|
| Anomaly detection | GL entries, transaction logs, user activity | Unusual journal postings, off-hours access |
| Supervised ML | Labelled fraud/legitimate transactions | AP invoice fraud, payroll manipulation |
| Unsupervised ML | Unlabelled transaction clusters | Novel schemes, revenue recognition abuse |
| NLP + OCR | Invoice images, expense text, contracts | Forged invoices, duplicate claims |
| Graph analysis | Entity relationships, payment networks | Supplier collusion, fictitious vendors |
When evaluating vendors, ask for SHAP (SHapley Additive exPlanations) values or feature importance outputs. These explainability techniques show which data features drove each alert, which is what you need to justify an investigation decision and keep an audit trail.
- * *
Where AI fraud detection applies in day-to-day UK accounting practice
The techniques above are only useful if they map to real workflows. These are the main accounting use cases.
Journal-entry testing. The general ledger is the most common site of management fraud. AI scores every journal entry against criteria such as unusual posting times, round-number amounts, entries that reverse shortly after period end, and postings by users outside their normal approval authority. An AI application scanning millions of entries in seconds surfaces the handful that warrant investigation, rather than leaving auditors to sample a limited portion and hope they pick the right ones.
Accounts payable and receivable fraud. Duplicate invoices, fictitious suppliers, and payment diversion are perennial AP risks. AI cross-references invoice metadata, bank details, and vendor master records to flag duplicates and mismatches before payment runs. On the AR side, it monitors for unusual credit notes, write-offs, or lapping schemes where receipts are misapplied across customer accounts.
Payroll fraud. Ghost employees, inflated hours, and unauthorised rate changes are difficult to catch manually in large payrolls. AI compares payroll outputs against HR records, flags employees with no manager approval chain, and detects salary changes that fall outside the normal distribution for a role or grade.
Expense claim abuse. NLP and OCR analyse claim narratives and receipt images, flagging duplicate submissions, personal expenditure disguised as business costs, and claims that exceed policy limits. The system can also detect clusters of claims submitted just below approval thresholds, a classic split-claim tactic.
!Close-up of hands verifying expense claim and receipt
Revenue recognition manipulation. Unsupervised models detect unusual patterns in revenue timing, such as a spike in end-of-quarter bookings that reverse in the following period, or contract modifications that accelerate recognition in ways inconsistent with prior periods.
Supplier diversion fraud. Graph analysis identifies when bank account details on the vendor master have been changed shortly before a large payment, or when a new supplier shares contact details with an existing employee.
The process flow is consistent across use cases:
- Ingest structured data (GL, AP/AR, payroll, bank feeds) and unstructured data (invoice images, expense receipts).
- Score each transaction or document against the relevant model.
- Triage alerts by risk score, routing high-priority items to investigators immediately.
- Investigate flagged items, gathering corroborating evidence.
- Capture the outcome (confirmed fraud, false positive, or inconclusive) and feed it back to refine the model.
- * *
How auditors and forensic accountants use AI in practice
For internal audit, the practical shift is from reactive investigations to continuous monitoring. That affects the audit calendar, staffing and documentation.
A typical AI-assisted investigation follows this sequence:
- Alert review. The auditor receives a prioritised alert queue. Each alert carries a risk score, the features that drove it (via SHAP or equivalent), and links to the underlying transactions.
- Data pull. Pull the full transaction history for the flagged entity, including related parties identified by graph analysis.
- Model explanation review. Confirm which features the model weighted most heavily. If the alert was driven by a posting time anomaly, verify whether there is a legitimate business reason (for example, a time-zone difference for an overseas subsidiary).
- Corroborating evidence. Cross-reference with HR records, vendor master, bank statements, and any relevant correspondence. NLP tools can assist with document review at scale.
- Escalation decision. If corroborating evidence supports the alert, escalate to the fraud investigation team or external authorities. Document the decision rationale explicitly.
- Outcome logging. Record the outcome against the alert. Confirmed fraud updates the model; false positives refine the detection parameters.
Before going live on current data, test the model against historical engagements where fraudulent entries are already confirmed. That gives the audit team its own precision and recall figures to present to the audit committee, rather than asking them to trust a black box.
AI augments rather than replaces auditors; human oversight is mandatory and the auditor remains responsible for interpretation and final judgement. The model surfaces candidates; the auditor decides.
- * *
What data and model quality do you need to evaluate?
Good fraud detection depends on good data. Before you commit to a vendor or build an in-house model, audit your data estate against these requirements.
Typical data sources for accounting fraud models:
- General ledger: posting user, timestamp, amount, account code, reversal flag.
- AP/AR ledgers: invoice metadata, vendor bank details, payment dates, credit note history.
- Payroll feeds: employee ID, role, grade, approval chain, payment amounts, change logs.
- Bank transaction data: reference, counterparty, amount, channel.
- Document images: invoice scans, receipt images, contract PDFs (processed via OCR).
- User activity metadata: login times, IP addresses, approval sequences.
Class imbalance and labelling. Fraud is rare relative to legitimate activity, which means models trained naively will learn to predict "legitimate" for almost everything and still achieve high accuracy. Techniques such as synthetic minority oversampling (SMOTE), cost-sensitive learning, and anomaly scoring address this. Labelling is also a challenge: many historical fraud cases are unconfirmed or partially documented, so your training set may be smaller than it looks.
Build a holdout test set from confirmed historical fraud cases before model training starts, and keep it separate from the training data. It is the dataset you use to check vendor claims and report detection rates to your audit committee.
Modern AI models continuously self-learn: false positives refine detection parameters and confirmed fraud updates model logic to catch similar future patterns. That lifecycle requires governance: who approves a model update, how is the change logged, and what triggers a full revalidation?
| Validation check | What to verify | Frequency |
|---|---|---|
| Backtesting on historical fraud | Precision and recall on confirmed cases | Before go-live and after major updates |
| Holdout set performance | Detection rate on unseen labelled data | Quarterly |
| Drift monitoring | Feature distribution shifts vs. training baseline | Monthly |
| Audit trail completeness | All alerts, decisions, and outcomes logged | Continuous |
| Bias assessment | Alert rates by supplier type, employee group | Bi-annually |
- * *
What AI adds to fraud detection, and where it falls short
Both sides belong in your business case.
Benefits:
- Scale. AI can score the whole population of journal entries and transactions rather than a sample.
- Continuous monitoring. Real-time risk management replaces periodic audit cycles, so fraud is detected during the period rather than at year-end.
- Pattern discovery. Unsupervised models find fraud schemes that no rule set anticipated, including novel attack patterns that supervised models trained on historical data would miss.
- Reduced manual workload. Investigators focus on high-risk alerts rather than manually reviewing large transaction populations.
Limitations:
- False positives. Every alert that turns out to be legitimate costs investigator time. Reducing the false positive rate is as operationally important as catching fraud, because a system that cries wolf too often gets ignored.
- Explainability gaps. Complex models, particularly deep neural networks, can be difficult to explain to an audit committee or a court. Explainability tools help but do not fully resolve this.
- Bias risks. If training data reflects historical investigation patterns, the model may over-flag certain supplier types or employee groups. Regular bias audits are necessary.
- Adversarial fraud. Sophisticated fraudsters can learn to mimic legitimate behaviour once they understand the detection logic, particularly if the model's features are predictable.
- Data quality dependence. Incomplete vendor master records, inconsistent chart of accounts, or missing metadata all degrade model performance.
The practical challenge is reducing false positives while keeping latency low in real-time scoring contexts. Precision measures the proportion of alerts that are genuine fraud; recall measures the proportion of actual fraud cases that are caught. Raising one typically lowers the other. Your acceptable trade-off depends on the cost of a missed fraud versus the cost of an unnecessary investigation. Agree a target false positive rate as part of your pilot acceptance criteria, based on how many alerts your team can realistically review, and track it weekly.
- * *
A practical pilot checklist for UK accounting teams
Running a structured pilot before full deployment protects you from committing to a system that does not fit your data or your workflows. Work through these steps in order.
- Define scope. Choose one high-risk process: AP invoice fraud is a common starting point because the data is structured and fraud patterns are well documented.
- Assemble and clean your data. Pull as much clean historical transaction data as you have, ideally covering more than one year-end. Identify and resolve gaps in vendor master records, user IDs, and approval metadata.
- Establish baseline metrics. Before the AI runs, document your current false positive rate (from manual review), average time-to-detection for known cases, and investigator hours per case.
- Choose your model type. For a first pilot, an anomaly detection approach requires no labelled fraud data and delivers results quickly. Add supervised models once you have a labelled holdout set.
- Run a parallel test. Operate the AI alongside your existing controls for at least one full month-end cycle, ideally a quarter. Do not replace manual review yet; compare outputs.
- Measure KPIs. Track precision, recall, false positive rate, time-to-detection, and investigator workload weekly.
- Governance sign-off. Present results to the audit committee with a written model explanation, a bias assessment, and a DPIA (see the regulatory section below). Get formal sign-off before moving to production.
Vendor evaluation questions to ask:
- What data access does the system require, and how is it transmitted and stored?
- Can you provide SHAP values or equivalent feature importance outputs for every alert?
- How often is the model retrained, and who approves each update?
- What is the typical latency from transaction ingestion to alert generation?
- How does the system integrate with our existing accounting platform (API, connector, batch extract)?
- What are the pricing components, and are there per-alert or per-transaction fees?
Pilot acceptance criteria:
- Precision and recall on the holdout test set at or above the targets you agreed before the pilot, and a false positive rate your team can keep up with.
- No material increase in investigator workload versus baseline.
- Full audit trail for every alert, decision, and outcome.
For practical guidance on embedding fraud prevention within an information security management framework, the ISMS fraud prevention guide is worth reading alongside your pilot planning.
- * *
UK regulatory, data protection, and ethical requirements
Deploying AI for fraud detection in the UK touches several overlapping frameworks. Sort these out before go-live.
Key regulatory considerations:
- ICO guidance on automated decision-making. Under UK GDPR, individuals have rights regarding solely automated decisions that significantly affect them. If your system automatically blocks a payment or flags an employee without human review, you need a lawful basis and a documented human-in-the-loop process. The ICO's guidance on Article 22 is the starting point.
- FCA expectations for regulated firms. The FCA expects firms to have documented, explainable controls for financial crime risk. Maintain model documentation, version history, and performance records.
- Audit trail requirements. Every alert, investigation step, and outcome must be logged with timestamps and user IDs. This is both a regulatory requirement and a practical necessity for any subsequent legal proceedings.
- Data Protection Impact Assessment (DPIA). A DPIA is mandatory under UK GDPR when processing is likely to result in a high risk to individuals, which AI-based fraud monitoring of employee or customer data almost certainly does. Complete the DPIA before you start processing and review it annually.
- Records of processing activities. Update your Article 30 records to reflect the new processing activity, including the legal basis, data categories, retention periods, and third-party processors involved.
Involve your Data Protection Officer and legal counsel before you sign a vendor contract. The data processing agreement, sub-processor list and international transfer mechanisms all need review, and gaps are easier to fix during procurement than after go-live.
Ethics checklist:
- Bias testing completed across supplier types, employee demographics, and transaction categories.
- Data use is proportionate: collect only what the model needs, not everything available.
- Human-in-the-loop oversight is documented and enforced: no automated action without a human decision point.
- Transparency obligations met: where individuals have a right to know they are subject to monitoring, that disclosure is in place.
- Model governance policy approved by the audit committee, covering retraining, version control, and incident response.
- * *
How do you measure whether the programme is working?
Metrics give you the evidence to defend the investment and show where the system needs tuning.
Core metric definitions:
- Precision: of all alerts generated, what proportion were genuine fraud? Low precision means investigators waste time on false positives.
- Recall: of all actual fraud cases in the period, what proportion did the system catch? Low recall means fraud is slipping through.
- False positive rate: the proportion of legitimate transactions flagged as suspicious. This drives operational cost and investigator fatigue.
- Time-to-detection: the elapsed time from when a fraudulent transaction occurs to when an alert is generated and reviewed.
- Reviewer workload: average number of alerts per investigator per week. A rising workload without a rising fraud rate suggests the model needs tuning.
- Cost per case: total investigation cost divided by confirmed fraud cases. Tracks efficiency over time.
- Loss reduction: the value of fraud prevented or recovered, compared to the pre-AI baseline.
| KPI | Reporting cadence | Target (pilot phase) |
|---|---|---|
| Precision | Weekly | Agreed before the pilot |
| Recall | Weekly | Agreed before the pilot |
| False positive rate | Weekly | Within what your team can review |
| Time-to-detection | Weekly | Reduction vs. baseline |
| Reviewer workload | Weekly | No material increase |
| Cost per case | Monthly | Trending downward |
| Loss reduction | Quarterly | Positive vs. pre-AI baseline |
Link these metrics to a simple dashboard reviewed at the weekly triage meeting and reported to the audit committee monthly. The monthly report should include a precision/recall trend chart, the top five alert categories by volume, and a narrative on any model updates made in the period.
- * *
Where can UK accounting teams find AI fraud detection tools?
The market splits into four broad categories, each with different integration profiles and cost structures.
- Integrated accounting platform features. Xero, Sage, and QuickBooks increasingly embed anomaly detection and duplicate-invoice flagging directly into their platforms. These are the lowest-friction starting point for smaller practices because they require no separate data pipeline.
- Specialist fraud analytics vendors. Dedicated fraud analytics platforms offer more sophisticated models, graph analysis, and configurable alert workflows. They typically connect via API or batch data extract and require more implementation effort, but deliver greater depth for complex or high-volume environments.
- Document verification and OCR providers. Vendors focused on invoice and receipt processing use OCR and NLP to verify document authenticity, extract structured data, and flag anomalies in document metadata. These pair well with AP automation workflows.
- Managed service partners. Some firms prefer to outsource fraud monitoring to a managed service that provides both the technology and the analyst resource. This suits organisations without an in-house data science capability.
Before shortlisting vendors, map your integration requirements: which accounting platform you run, what data formats it exports, and whether your IT team supports API connections or only batch file transfers. A strong model is no use if it cannot connect to your data.
The AI Ledger's directory of 300+ AI tools for accountants and bookkeepers covers these categories, and the audit and fraud detection category narrows it to the relevant tools. Each listing has an editor score, a verdict and a last verified date, and scores are never for sale. If you want a shortlist matched to your accounting platform and practice size, use the finder.
- * *
Key takeaways
| Point | Details |
|---|---|
| Core definition | AI fraud detection builds dynamic baselines across accounting data and flags anomalies for human review, instead of relying only on static rules. |
| Techniques to prioritise | Start with anomaly detection, which needs no labelled fraud data; add supervised models and graph analysis as your labelled dataset grows. |
| Pilot approach | Run a parallel test on one process, such as AP invoices, and measure precision and recall before go-live. |
| Compliance essentials | Complete a DPIA, update Article 30 records, and document human-in-the-loop oversight before processing live data under UK GDPR. |
| Finding tools | Start with the audit and fraud detection category or the finder. |
- * *
Getting the groundwork right
The teams that get the most from AI fraud detection are usually the ones that did the unglamorous work first: cleaning the vendor master, standardising the chart of accounts, building a labelled holdout dataset from historical cases, and agreeing an escalation protocol before the first alert fires. Without that, a high-recall model produces a queue of alerts that nobody has the process or authority to investigate.
There is also a people side. Investigators with years of professional judgement can see automatic scoring as a threat. Design the workflow so the model takes away the manual population review and leaves the corroboration and escalation decisions with them, and say so plainly. Plan for the roles that change: someone who owns the data pipeline and model governance, someone who interprets model outputs and manages retraining, and investigators who focus on corroboration rather than initial detection.
- * *
Useful sources for UK auditors
- ICO guidance on automated decision-making and profiling covers Article 22 rights and the conditions under which automated decisions affecting individuals are lawful. Read it before deploying any AI system that influences fraud investigations involving employees or customers.
- EY: How an AI application can help auditors detect fraud provides a practitioner-level overview of AI-assisted journal-entry testing and how audit teams validate model outputs against historical fraud cases.
- Journal of Accountancy: AI and fraud, what CPAs should know addresses the human-in-the-loop requirement and the professional responsibilities auditors retain when AI is part of the detection workflow.
- IBM: What is fraud detection? gives a clear technical explanation of supervised and unsupervised approaches, useful background for auditors evaluating vendor model architectures.
- Stripe: AI for fraud detection covers model lifecycle management, including how false positives feed back into retraining and why explainability methods such as SHAP matter for auditability.
_This article is general information for accounting and auditing professionals and does not constitute legal, regulatory, or professional advice. Confirm current ICO, FCA, and UK GDPR requirements with your Data Protection Officer or a qualified legal adviser before deploying AI fraud detection systems._
Recommended
- Why AI reduces accounting errors: a 2026 guide)
- Accountant AI tool comparison guide for 2026)
- Machine learning accounting basics: a 2026 guide)
- AI in accounting explained: the 2026 professional guide